1 Why authorization matters: Securing access in a digital world
Authorization is presented as a foundational capability for modern digital systems rather than a narrow security feature. The chapter opens with the Target breach to show how weak access boundaries, poor visibility, and slow response can turn a single compromised vendor account into a massive incident. It then explains that digital identity systems exist to manage relationships: authentication identifies who is making a request, accounts store what the system remembers about them, and authorization determines what they are allowed to do.
The text argues that traditional access control methods such as ACLs, groups, and roles are too static for today’s cloud, SaaS, distributed, and multi-tenant environments. They struggle with scale, flexibility, maintainability, efficiency, auditability, security, and consistency, often leading to policy drift and hidden complexity. In contrast, dynamic authorization evaluates policies at runtime and can respond to context such as device posture, time, location, department, consent, and risk, making access decisions more precise and easier to govern.
The chapter’s broader message is that authorization now shapes business outcomes as much as it shapes security. By treating policies as either code or data, organizations can reduce operational overhead, support changing customer needs, strengthen compliance, improve user experience, and adapt to new realities like zero trust, IoT, and AI agents. The result is a strategic shift: authorization becomes an explicit architectural layer that helps organizations move faster while staying in control of trust and access.
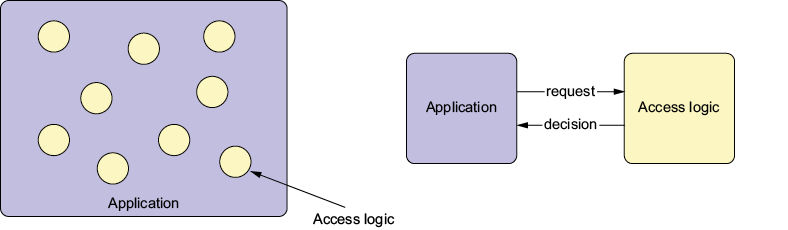
Embedding access logic throughout application code (left) creates tight coupling. Externalizing authorization into a separate component (right) makes access policies explicit, decouples decision-making from application behavior, and enables scalable, auditable access control.
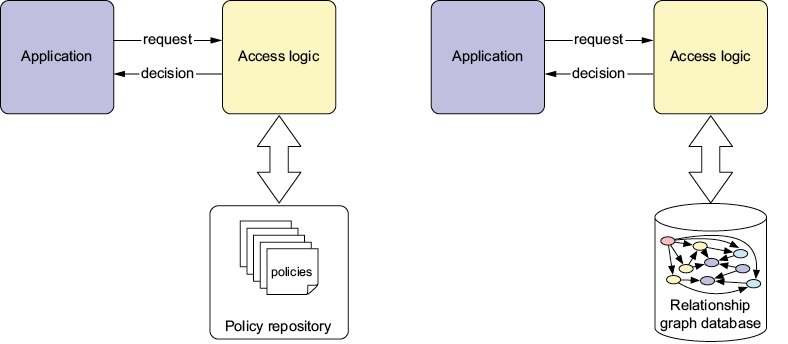
Dynamic authorization can represent policy in two complementary ways. On the left, Policy as Code stores machine-readable policies in a repository that the access logic evaluates at runtime. On the right, Policy as Data stores relationships and attributes in a structured data store that the same access logic uses to determine decisions. Both approaches externalize policy from the application, while supporting different kinds of flexibility.
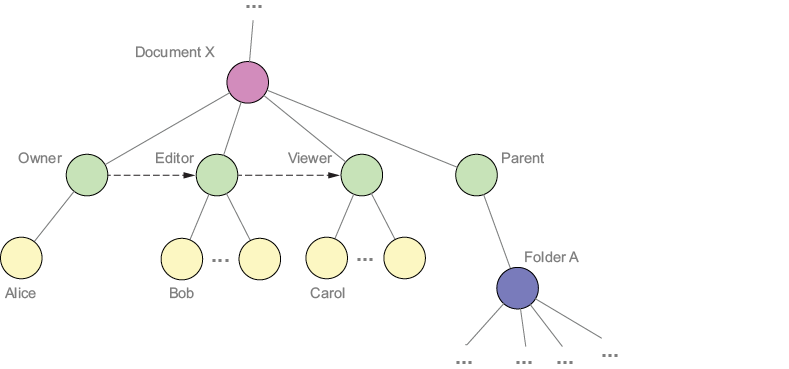
A relationship graph representing access to a Google document. Rather than using static ACLs, this model captures roles (e.g., Owner, Editor, and Viewer) as first-class relationships between users and resources. The graph also models hierarchical relationships, such as parent folders, enabling more flexible, general-purpose authorization logic that can be queried and evaluated dynamically.
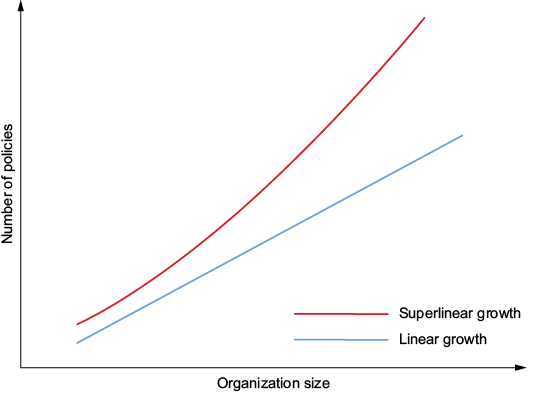
As an organization grows, the number of access policies tends to increase faster than linearly. Although a small organization might manage with a simple, flat set of policies, larger organizations face compounding complexity due to team structures, regional compliance, and overlapping responsibilities, leading to superlinear policy growth.
Summary
- Poor access control can lead to severe security breaches, as seen in the Target breach, where attackers exploited weak authorization to access sensitive systems.
- Authorization is not just about security; it also enables key features in modern cloud applications, such as document sharing and multi-tenant access control.
- Traditional authorization methods such as ACLs and RBAC are static and struggle with scalability, flexibility, maintainability, efficiency, auditability, and security.
- Dynamic authorization overcomes these challenges by using policies to make real-time, context-aware access decisions.
- Policy-based access control (PBAC) enables fine-grained authorization by externalizing access control logic, making it dynamic and adaptable to changing conditions.
- The shift toward zero-trust security models, SaaS applications, IoT, regulatory compliance, and AI-driven applications demands more flexible and scalable access control, making dynamic authorization essential.
- Policies can be represented as code or data, enabling both structured rule enforcement and flexible, real-time access adjustments.
- Treating Policy as Code allows version control, testing, and automation, while Policy as Data supports fine-grained, user-defined access controls.
- Organizations adopting dynamic authorization benefit from reduced operational costs, improved agility, enhanced security, and better customer experiences.
- Businesses can use dynamic authorization as a competitive advantage, enabling new product capabilities, faster compliance adaptation, and stronger security.
- Authorization is a strategic investment, not just a security measure; organizations that adopt policy-based access control gain efficiency, scalability, and security.

 Authorization in Action ebook for free