1 Governing Generative
Generative AI is already transforming work by writing, coding, and creating on demand, but the chapter stresses that its speed and flexibility also amplify failures, from hallucinated legal citations to data leaks, prompt injections, and deepfakes. Because these systems can be used instantly across many contexts, traditional governance approaches built for predictable software no longer suffice. The central message is that organizations need a new way to manage risk that recognizes GenAI’s scale, unpredictability, and ability to cause public, legal, financial, and reputational harm very quickly.
The chapter explains that governance, risk management, and compliance for AI are not just about ticking boxes; they are essential for turning AI into something trustworthy and sustainable. Governance sets direction and accountability, risk management continuously identifies and reduces AI-specific threats, and compliance ensures alignment with laws, regulations, and internal commitments. Yet compliance alone is not enough, because a system can be formally compliant and still unsafe or unfair in practice. Effective AI governance must be built into daily work from the beginning, not added after deployment, and it must adapt as models, threats, and regulations evolve.
To make this practical, the chapter proposes a lifecycle-based framework for GenAI governance that runs from strategy and risk assessment through design, testing, deployment, monitoring, and retirement. This model emphasizes layered controls, continuous evaluation, and shared responsibility across model developers, integrators, and users. It also shows why GenAI requires new tools such as threat modeling, red teaming, output filters, monitoring dashboards, and feedback loops for improvement. The overall takeaway is that responsible AI innovation is possible, but only when organizations treat governance as an ongoing operating discipline rather than a one-time review.
Generative models such as ChatGPT can often produce highly recognizable versions of famous artwork like the Mona Lisa. While this seems harmless, it illustrates the model's capacity to memorize and reconstruct images from its training data; a capability that becomes a serious privacy risk when the training data includes personal photographs.
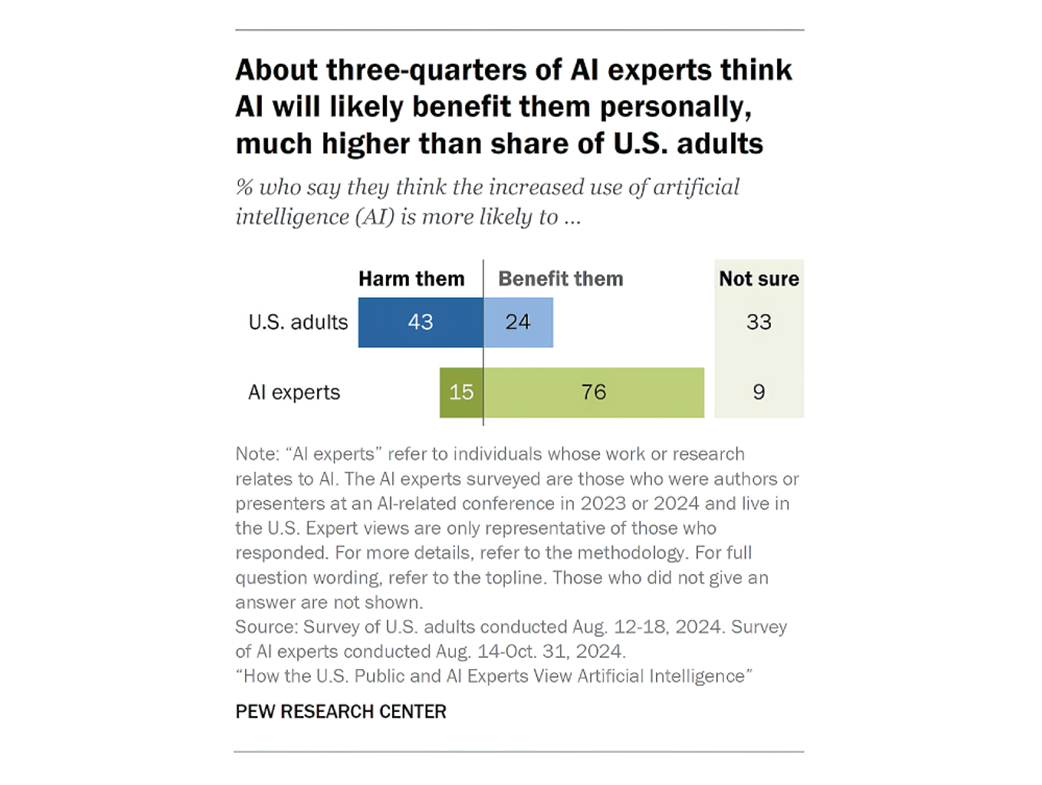
Trust in AI: experts vs general population. Source: Pew Research Center[46].
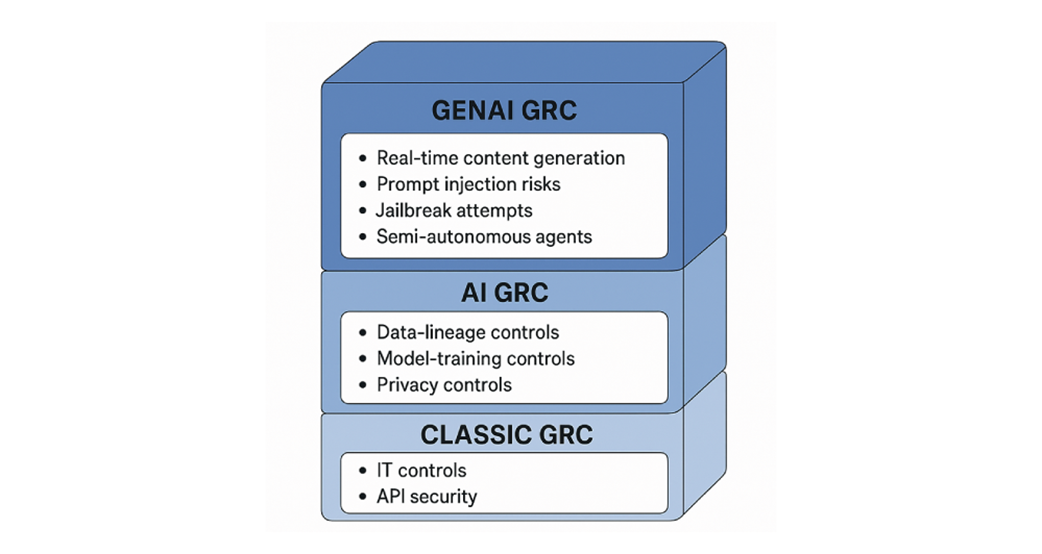
Classic GRC compared with AI GRC and GenAI GRC
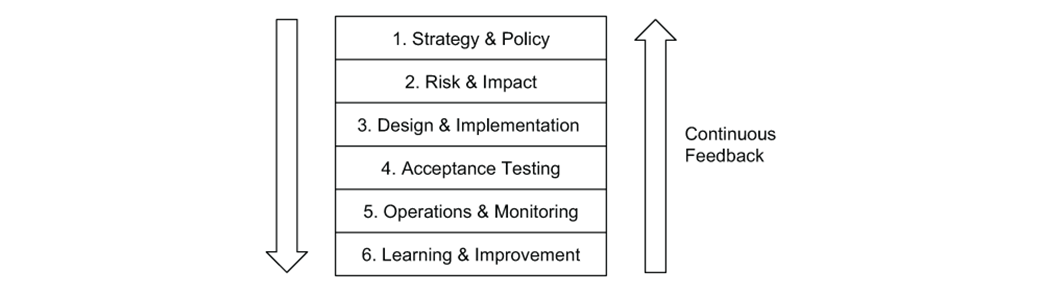
Six Levels of Generative AI Governance. Chapter 2 will expand into what control tasks attach to each checkpoint.
Summary
- GRC for generative AI is not a dry compliance exercise, but it is an active, risk informed, ongoing discipline that requires involvement from legal to engineering.
- The Six-Level Governance (6L-G) model spans the AI lifecycle and multiple layers of risk, making sure critical issues aren’t missed. The model gives you that lifecycle structure (strategy, risk assessment, implementation, testing, operations, improvement), catching issues where they're still cheap to fix.
- Many risks cut across the org chart: hallucination, prompt injection, model theft, and data deletion obligations. These touch security, privacy, legal, and product all at once, so no single team owns the problem on its own.
- We have also provided a teaser of the tools and practices that can address those challenges, giving you a sense that this is manageable with the right approach.

 AI Governance ebook for free