Elliptic curve cryptography is presented as a practical answer to modern security needs, especially for developers who want stronger public-key systems with smaller numbers and lower resource costs than older approaches like RSA. The chapter introduces the basic idea that public key cryptography lets two parties safely create a shared secret over an open network, then use that secret with a fast symmetric cipher such as AES. It also explains the core roles of private keys and public keys in encryption, authentication, and digital signatures, showing how these tools support secure messaging, trusted documents, and anonymous or privacy-preserving transactions.
The chapter then builds toward the special value of elliptic curves in advanced applications. It emphasizes that elliptic curves are widely used in real systems such as payment protocols, web certificates, healthcare, supply chains, and blockchain environments. Beyond ordinary key exchange and signatures, the text highlights pairing-based elliptic curve methods, which make aggregate signatures and zero-knowledge proofs possible in compact and efficient ways. These pairing operations are described as mathematically deeper than basic curve arithmetic, but also as the key to many modern cryptographic constructions that are difficult or impossible to match with other techniques.
The chapter closes by framing the book’s purpose and audience. It acknowledges that the math can be challenging, but argues that readers do not need to be advanced mathematicians if they are willing to learn step by step. The book aims to guide developers through the necessary algebra, finite fields, and curve concepts so they can understand and implement secure cryptographic algorithms, including pairing-based schemes. In short, it sets expectations, motivates the subject with real-world use cases, and prepares the reader for a gradual path from basic elliptic curve ideas to the more sophisticated pairing methods used later in the book.
Conceptual elliptic curve over a finite field. Points are scattered in a multidimensional, astronomically large space.
Schematic of elliptic curve pairing with one point on base curve, one point on field extension curve, and the result in field extension values.
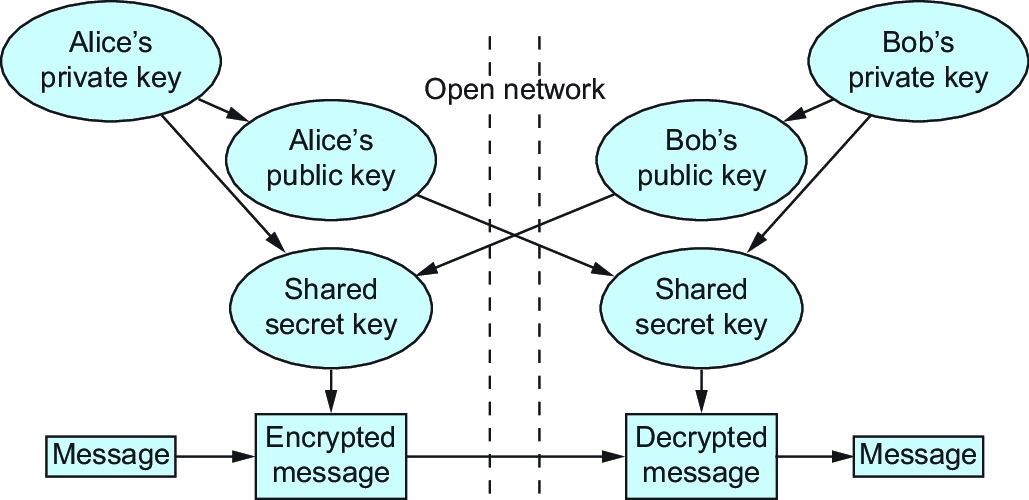
Creating a secret key by exchanging public keys
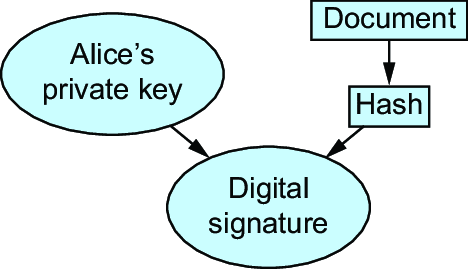
Processes involved with creating a digital signature
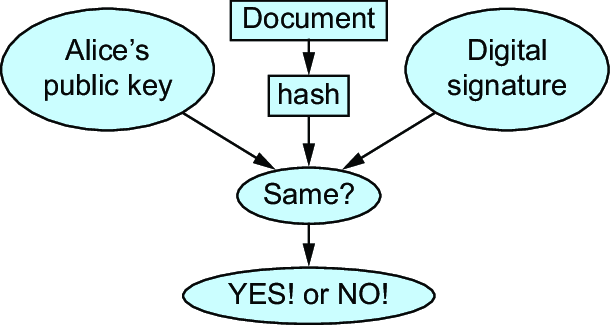
Process and data required to verify a digital signature
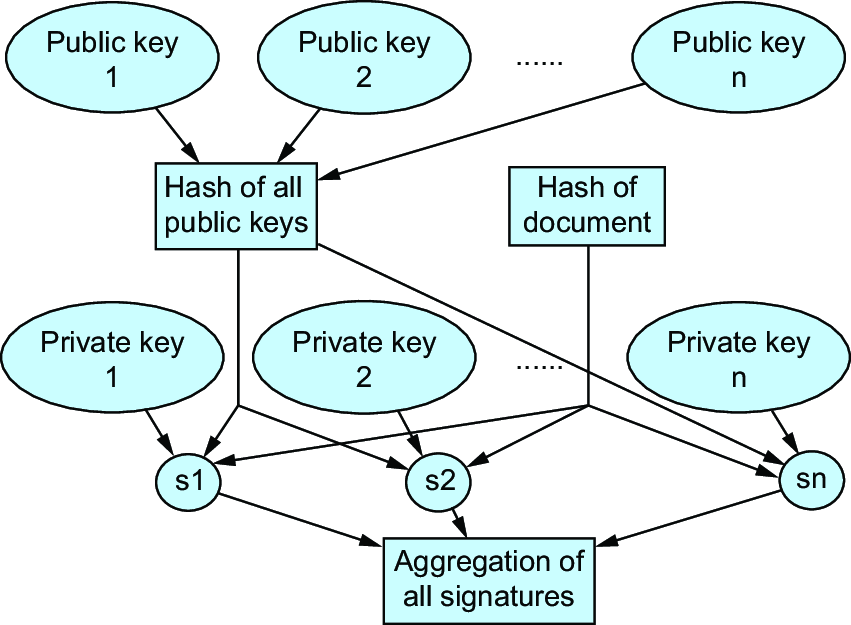
Aggregated digital signature signing combines multiple users’ public keys and individual signatures to create a single signature.
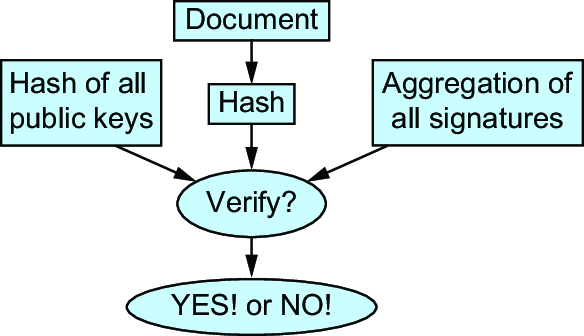
Aggregated digital signature verification process
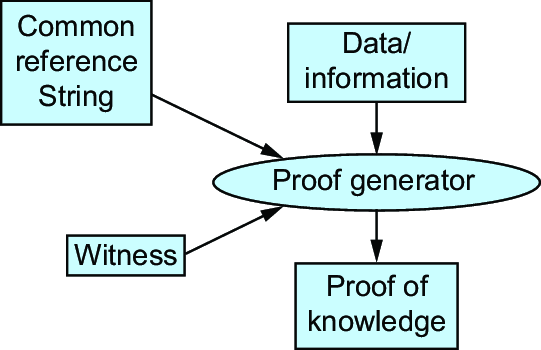
Requirements involved to create zero-knowledge proof
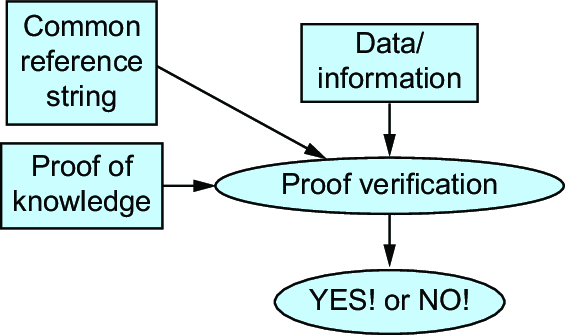
The process of verifying a zero-knowledge proof
Summary
Finite fields are sets with specific rules and a finite number of objects. The mathematics of finite fields determines how we manipulate elliptic curves.
Elliptic curves over finite fields are good for cryptography because they use smaller numbers for the same level of security compared with other public key methods.
Key exchange and digital signatures are straightforward, using elliptic curve mathematics through simple formulas. This makes programming the mathematics easy.
Aggregation of many digital signatures using pairings over elliptic curves allows for smaller storage on a blockchain than other methods. This reduces the amount of data transmitted between peers, which decreases over all transaction time.
Zero-knowledge proofs can certify knowledge of information without exposing that information. Zero-knowledge proofs use reduced amounts of data compared with other methods when using elliptic curve pairing mathematics.
FAQ
What is elliptic curve cryptography (ECC)?Elliptic curve cryptography is a public key cryptography method that uses mathematics based on elliptic curves over finite fields to create secure encryption, key exchange, and digital signatures. Its main advantage is that it can provide strong security with much smaller numbers than older systems like RSA.Why are elliptic curves considered useful for cryptography?They are useful because they offer the same security as other public key systems with smaller key sizes, which reduces memory use, processing time, hardware cost, and communication overhead. They also enable cryptographic features like aggregate signatures and zero-knowledge proofs that are difficult or impossible with some other methods.Why is it called an “elliptic curve” if there are no ellipses?The name comes from history, not from the shape of the curve. The term originated from formulas used in studying elliptical orbits in mathematics, and the label stayed even though the cryptographic objects are not literal ellipses or smooth curves in the usual sense.Where is ECC used in real-world applications?ECC is used in many places, including credit card transaction systems, SSL/TLS key exchange, certificate signing for websites and documents, HIPAA-related authentication, blockchain systems, healthcare, and supply chain environments.How does elliptic curve cryptography support public key exchange?Two parties each generate a private key and a corresponding public key. They share only the public keys, then combine their own private key with the other party’s public key to derive the same shared secret, which can then be used with a fast symmetric cipher such as AES.What is the role of digital signatures in ECC?Digital signatures let someone prove that they created a document and that the document has not been altered. The signer uses a private key to create the signature, and anyone can use the signer’s public key to verify it.How do aggregated digital signatures work?In an aggregated signature system, multiple public keys are combined, each signer creates a signature over the document and the aggregated keys, and then the signatures are mathematically combined into one final signature. Verification uses elliptic curve pairings to confirm that all signers signed the same document.What are zero-knowledge proofs, and why do they matter in ECC?Zero-knowledge proofs let someone prove they know private information without revealing the information itself. In ECC-based systems, they are especially important for privacy-preserving blockchain transactions and other settings where verification must be possible without exposing secrets.What are elliptic curve pairings used for in cryptography?Pairings map points on elliptic curves to values in a field extension, creating a relationship that is useful for advanced cryptographic schemes. They are central to technologies such as aggregate signatures and succinct noninteractive proofs, especially SNARKs.Who is this book meant for?This book is for developers who want to understand enough elliptic curve mathematics to implement common cryptographic algorithms, even if they do not have an advanced mathematics degree. It assumes some comfort with equations, polynomials, and basic linear algebra, and it builds toward pairing-based cryptography step by step.
pro $24.99 per month
access to all Manning books, MEAPs, liveVideos, liveProjects, and audiobooks!



 Elliptic Curve Cryptography for Developers ebook for free